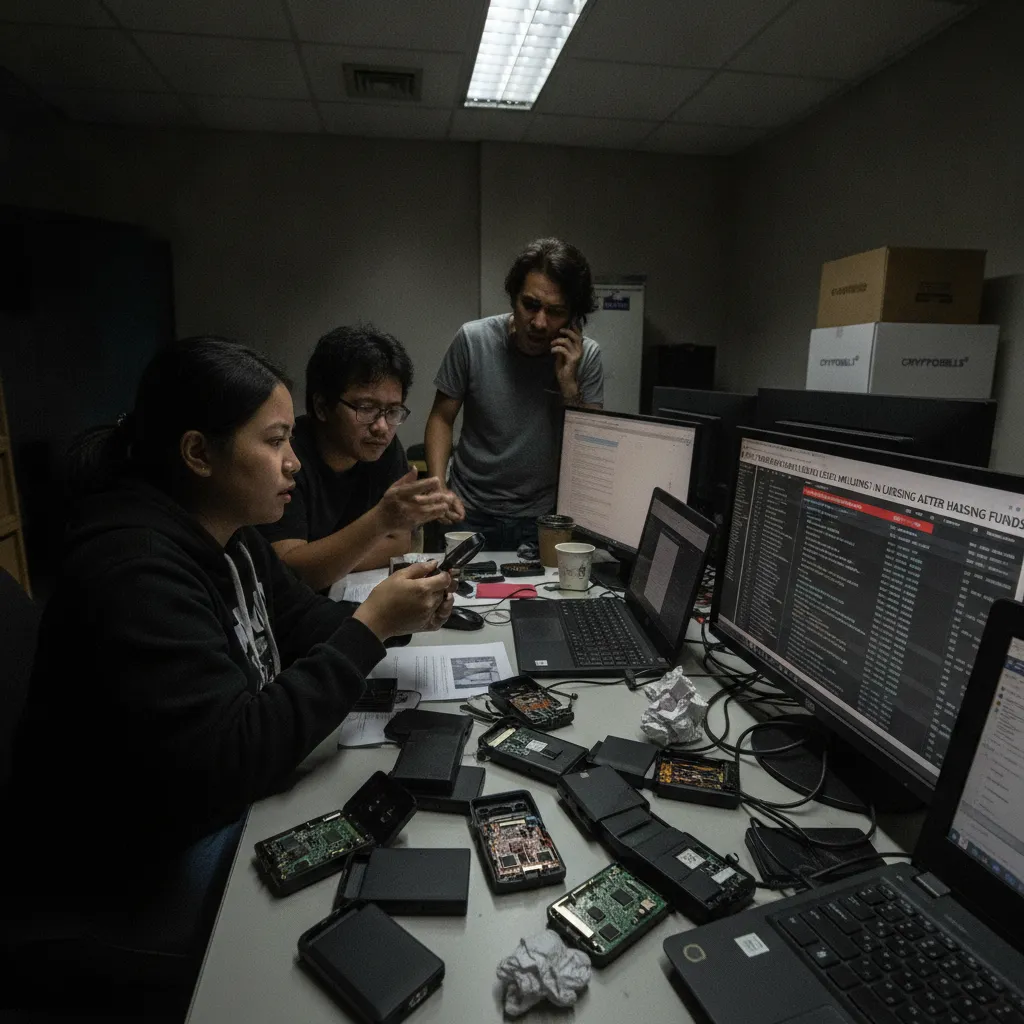
Hardware wallet giant Ledger has confirmed that at least one of its devices contained an unauthorized physical implant, providing a grim explanation for a massive wave of cryptocurrency thefts. All currently identified cases of tampering are linked to CryptoBilis, a reseller operating across Indonesia, Malaysia, and the Philippines. While Ledger insists that its own internal systems and direct sales channels were never compromised, the breach suggests a sophisticated attack on the product supply chain before the devices reached consumers.
The financial fallout is staggering, with independent on-chain researchers estimating that between 86 million and 93 million dollars vanished from more than 300 different wallets. This heist spans several major networks including Bitcoin, Ethereum, and Tron. In response to the discovery, CryptoBilis has halted all hardware sales while an investigation continues. Ledger is now urging any customer who bought a device from that specific reseller to stop using it immediately; those who have already initialized their wallets are being told to migrate their funds to a fresh seed on a device purchased directly from the manufacturer.
This incident reignites a heated debate over whether self-custody is truly as secure as promised. Since the collapse of FTX in 2022, millions of investors moved their assets off exchanges and into cold storage to avoid centralized risk. However, recent history shows these physical guards aren’t infallible, following a separate firmware flaw in Coldcard devices earlier this year that resulted in similar losses. The latest crisis highlights a growing vulnerability where hackers target the physical journey of a device rather than attempting to crack its digital encryption.
As investigators dig deeper into how the implants were installed, theories about corporate infiltration have begun to surface. Binance co-founder Changpeng Zhao suggested on social media that attackers may have actually acquired the reseller under false pretenses to facilitate the operation, though these claims remain unverified. Meanwhile, Ledger is calling for stricter industry wide standards for chain-of-custody practices and warns users to stay vigilant against secondary scams targeting victims of this breach.